Applied AI
39 articles · page 3 of 5
The Best Enterprise AI Feature Is a Well-Designed Exit
Production AI is judged less by how often it produces an answer than by what happens when it should not. Exception paths, reversibility, and human ownership are the architecture—not operational cleanup.
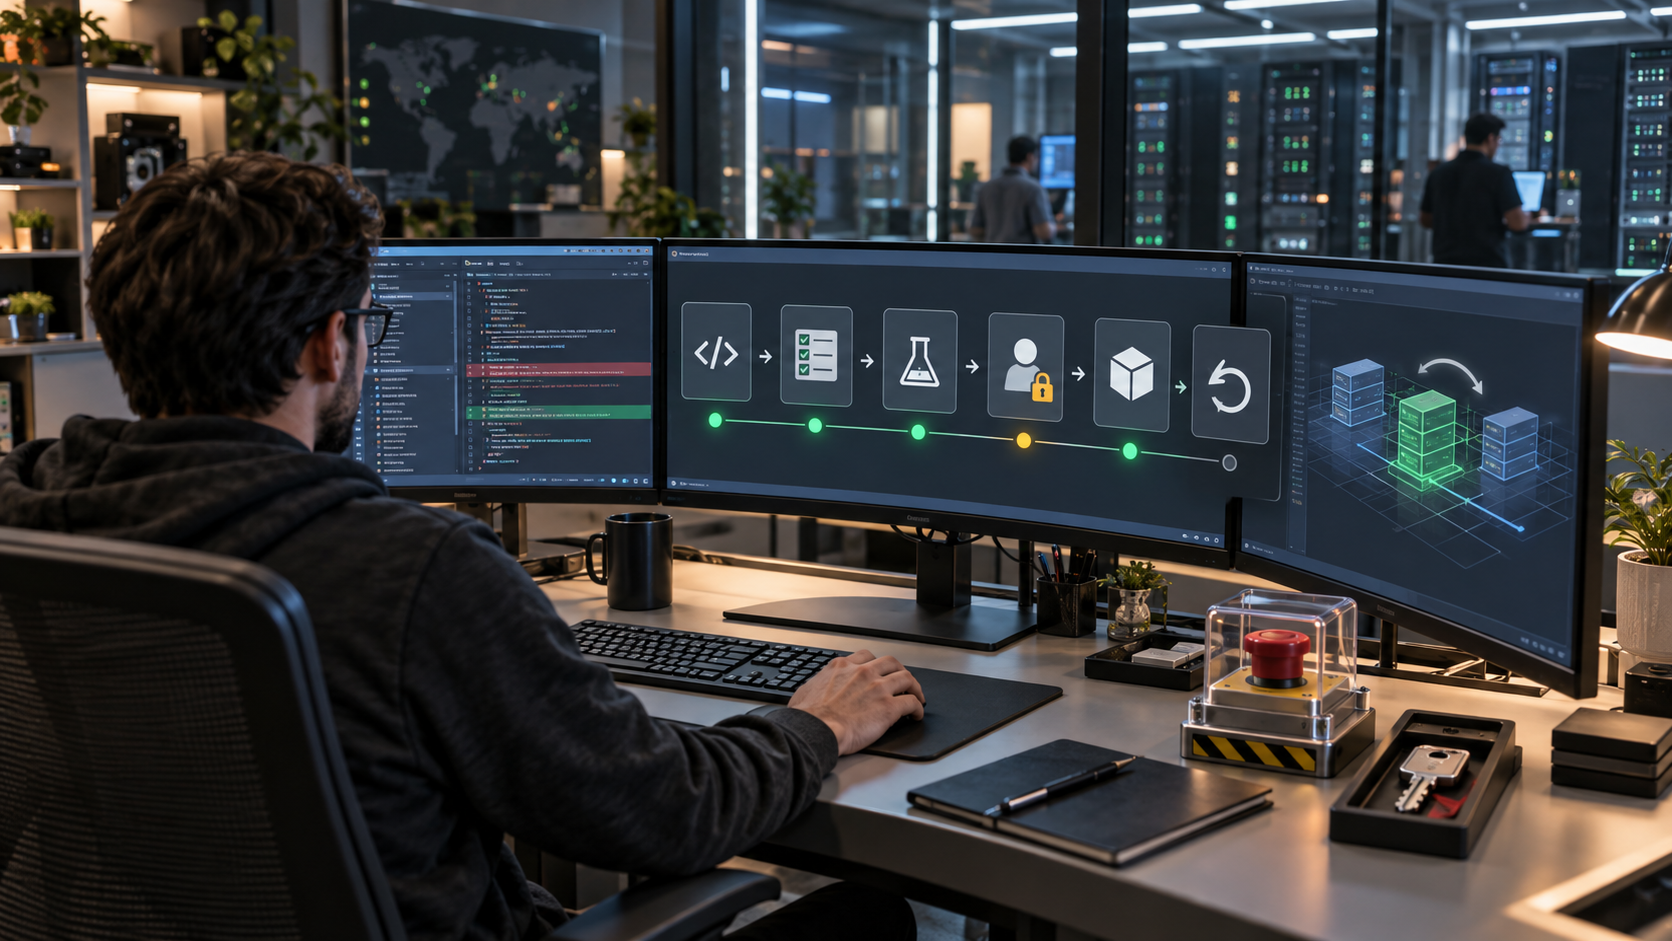
Stop Designing Coding Agents as Chatbots With Shell Access
A production coding agent is not primarily a conversational interface. It is a controlled operator whose real product surface consists of permissions, evidence, recovery, and handoff.
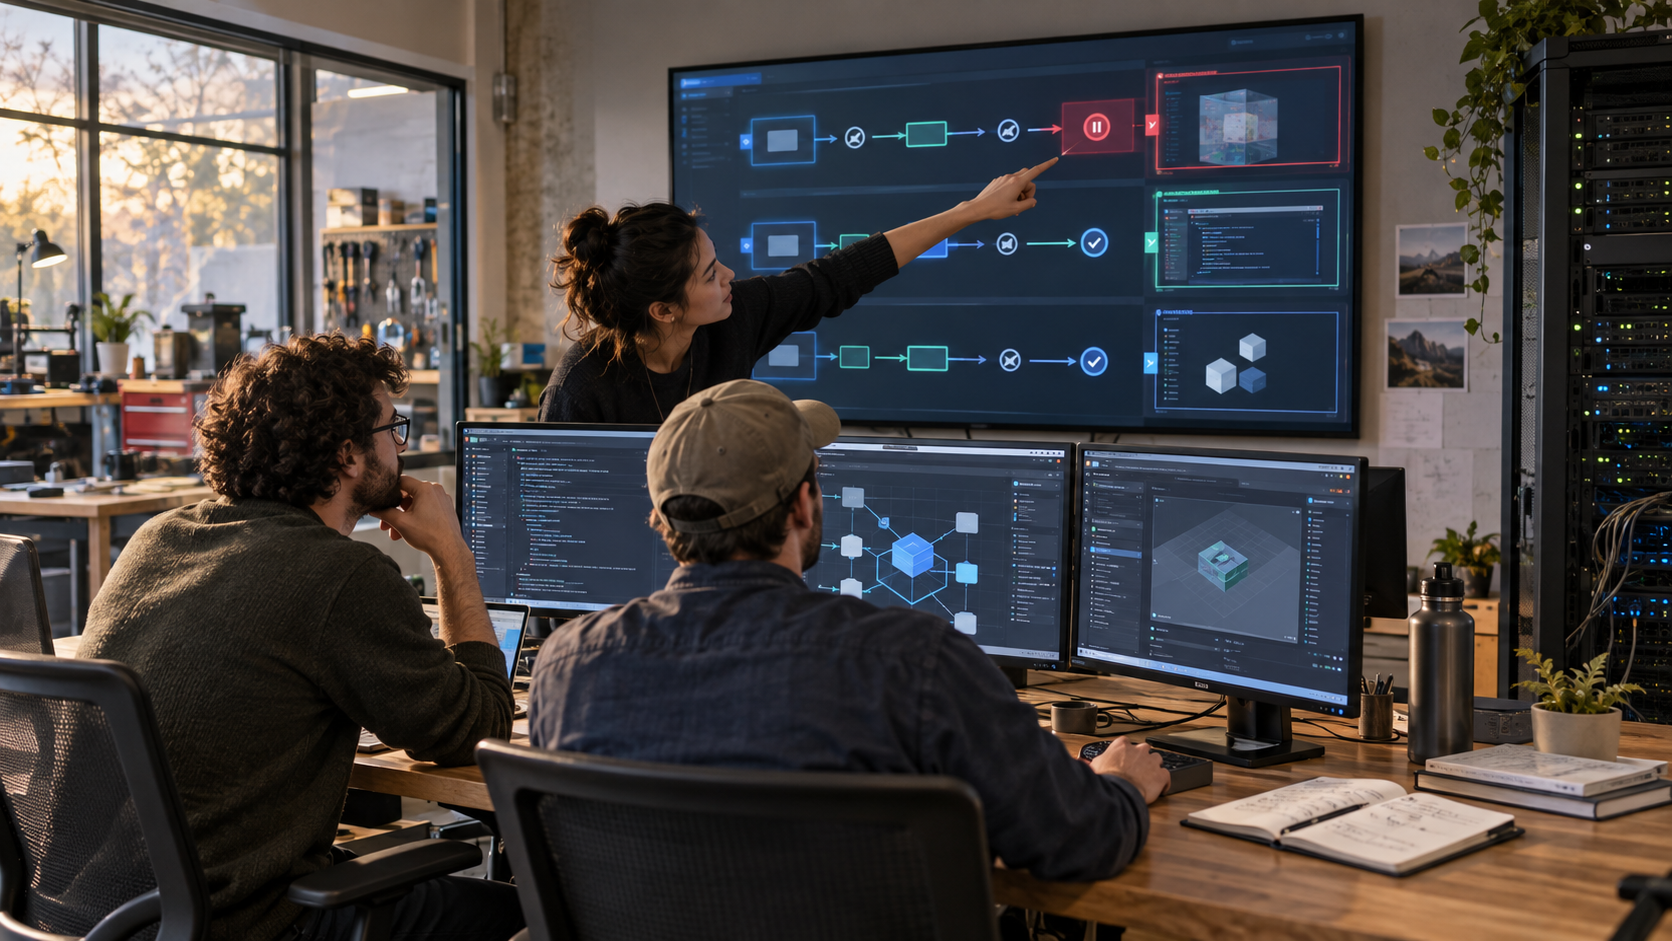
Stop Hiring AI Agents. Start Designing Their Jurisdiction.
An agent’s job description matters less than the boundaries around its tools, approvals, and responsibility. Teams should organize autonomous software around jurisdiction: what it may observe, change, spend, and commit.
Coding Agents Need Change Budgets, Not Blank Checks
The central risk of AI-assisted software development is not that agents write bad code; teams already know how to reject bad code. It is that they can create more plausible change than an organization can responsibly understand.
Give the Agent an Undo Button Before Giving It More Authority
Permission prompts are a poor substitute for operational safety. Useful AI agents need bounded actions, durable audit trails, and recovery paths designed into the workflow from the start.
Stop Giving Agents Job Titles; Give Them Permission Boundaries
Calling an AI system a “researcher” or “operations manager” hides the decisions that determine whether it is safe to deploy. Production agents need explicit authority, budgets, and reversible actions—not anthropomorphic roles.
Give Coding Agents a Budget of Authority, Not a Longer Prompt
The safest useful coding agent is not the one with the most elaborate instructions. It is the one whose permissions, evidence requirements and rollback paths make good behavior easier than improvisation.
Give AI Agents a Failure Budget, Not a Blank Check
Agent autonomy should be designed as a limited operational resource. The safest and most useful systems expand authority according to reversibility, evidence, and accumulated risk—not a single approval dialog.
The Best Coding Agent Leaves a Better Audit Trail Than Its Author
AI-generated code is not the hardest governance problem. The harder problem is reconstructing why a change was made, what evidence supported it, and which assumptions survived review.