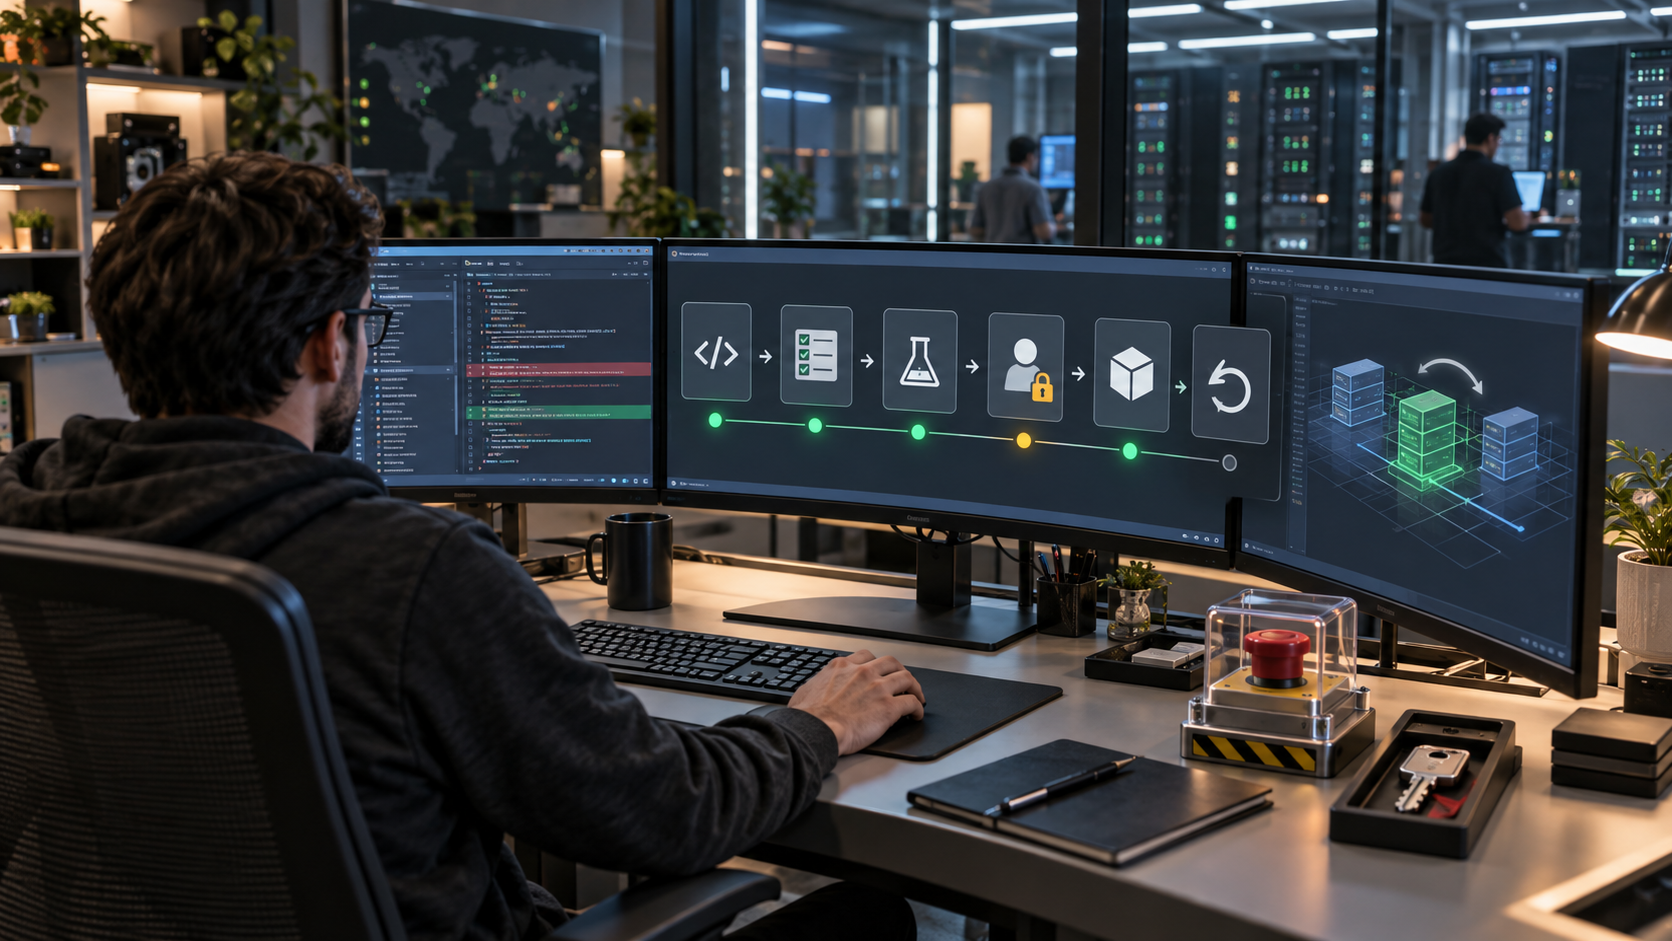
Many coding-agent products begin with the wrong mental model. A chat interface gains access to a repository and a terminal, then gradually accumulates tools until it can edit files, run tests, open pull requests, and deploy software. The result may look capable in a demo. In production it often feels like a talented contractor working without a badge system, change policy, or clear definition of done.
The better model is not “chatbot that can code.” It is “operator inside a controlled delivery environment.” Conversation remains useful, but it is not the foundation. The foundation is a set of explicit capabilities, observable state transitions, and recovery paths.
This distinction matters because software work changes shared systems. A plausible answer in a chat can be ignored. A plausible database migration can destroy data. The engineering challenge is therefore less about making the agent sound confident and more about ensuring that its authority is proportional to the evidence it has accumulated.
Permissions should describe effects, not tools
Most agent permission systems are organized around mechanisms: allow the terminal, permit network access, approve a command. Users, however, reason about effects. Reading application logs is different from downloading arbitrary code, even though both use the network. Running unit tests is different from publishing a package, even though both may use the same command-line program.
A strong system expresses authority in terms such as: read this repository; write only within this worktree; query this production service without mutation; create a draft pull request; request approval before changing external state. The agent should receive the narrowest capability that completes the current task, and that capability should expire with the task.
The security principle is familiar, but agents give it a usability dimension. Excessive prompts train people to approve reflexively. Unlimited access removes the moment when intent can be corrected. Good permission design puts friction at changes in consequence, not at every technical operation.
Anthropic’s engineering guidance on effective agents argues for simple, composable patterns and carefully designed tool interfaces. That advice is easy to underestimate. A tool description is not documentation around the product; for an agent, it is part of the product’s control plane. Ambiguous parameters, overloaded commands, and unstructured errors create behavioral uncertainty no model upgrade can fully erase.
Evidence should replace narration
Coding agents are verbose when they lack proof. They explain what they intended to change, summarize why it should work, and present a reassuring account of completion. None of that is equivalent to evidence.
A trustworthy handoff should be assembled from artifacts: the exact diff, tests executed, test results, static checks, commands that changed state, unresolved warnings, and assumptions that could not be verified. If a test was not run, the system should say why. If the repository was already dirty, it should distinguish prior edits from its own. If success depends on a service the agent could not access, that dependency should remain visibly open.
The SWE-bench task formulation helped move evaluation toward real repositories and executable outcomes. Product teams should carry that instinct into everyday use: prefer verifiable work over fluent descriptions of work. Yet passing tests are not sufficient. Tests can be incomplete, altered incorrectly, or disconnected from the architectural intent. Evidence needs hierarchy: automated checks establish a floor; human review evaluates whether the change belongs.
This suggests a different interface. Instead of making the transcript the primary object, make the task state primary. Show what the agent believes the goal is, which files it touched, what evidence supports completion, what approvals remain, and how to reverse the changes. Preserve the transcript for audit and diagnosis, but do not force users to read a small novel to discover whether a command failed.
Recovery is a first-class capability
Agent design tends to celebrate forward motion: planning, tool use, iteration, completion. Real software operations are defined just as much by recovery. Dependencies time out. Tests flake. Credentials expire. A branch moves while work is in progress. The user changes the requirement after seeing the first implementation.
An agent should know how to checkpoint, retry selectively, rebase its understanding, and stop without leaving a poisoned environment. Every consequential action needs an answer to four questions: Can it be previewed? Can it be made idempotent? Can it be reversed? Who must approve it?
Human oversight then becomes more precise. People should not have to supervise each keystroke. They should set the operating envelope, review transitions across risk boundaries, and judge decisions that require domain context. This resembles the practical pattern described in research on measuring agent autonomy: autonomy is not a single switch but a relationship between tool use, oversight, and consequence.
The best agent may look less magical
There is a commercial temptation to hide constraints because unrestricted demonstrations look impressive. But production users eventually encounter the constraints through failures. A tool that openly scopes its access, shows incomplete evidence, and asks for approval at meaningful boundaries may appear less autonomous while accomplishing more dependable work.
At XioX, we think coding agents should be judged by the quality of the system they leave behind, not the theatricality of the session. Did they preserve local changes? Did they improve or weaken maintainability? Can another engineer understand the patch? Is the result reproducible? Can the team recover quickly if the change is wrong?
The chat box will remain. It is a natural place to express intent and negotiate ambiguity. But it should sit above a rigorous operational substrate: capability-scoped tools, isolated workspaces, observable actions, evaluation gates, reversible changes, and evidence-rich handoffs. Once that substrate exists, better models become genuinely useful rather than merely more adventurous. The future coding agent is not a colleague trapped in a text window. It is a carefully governed participant in the software delivery system.
Advertisement


