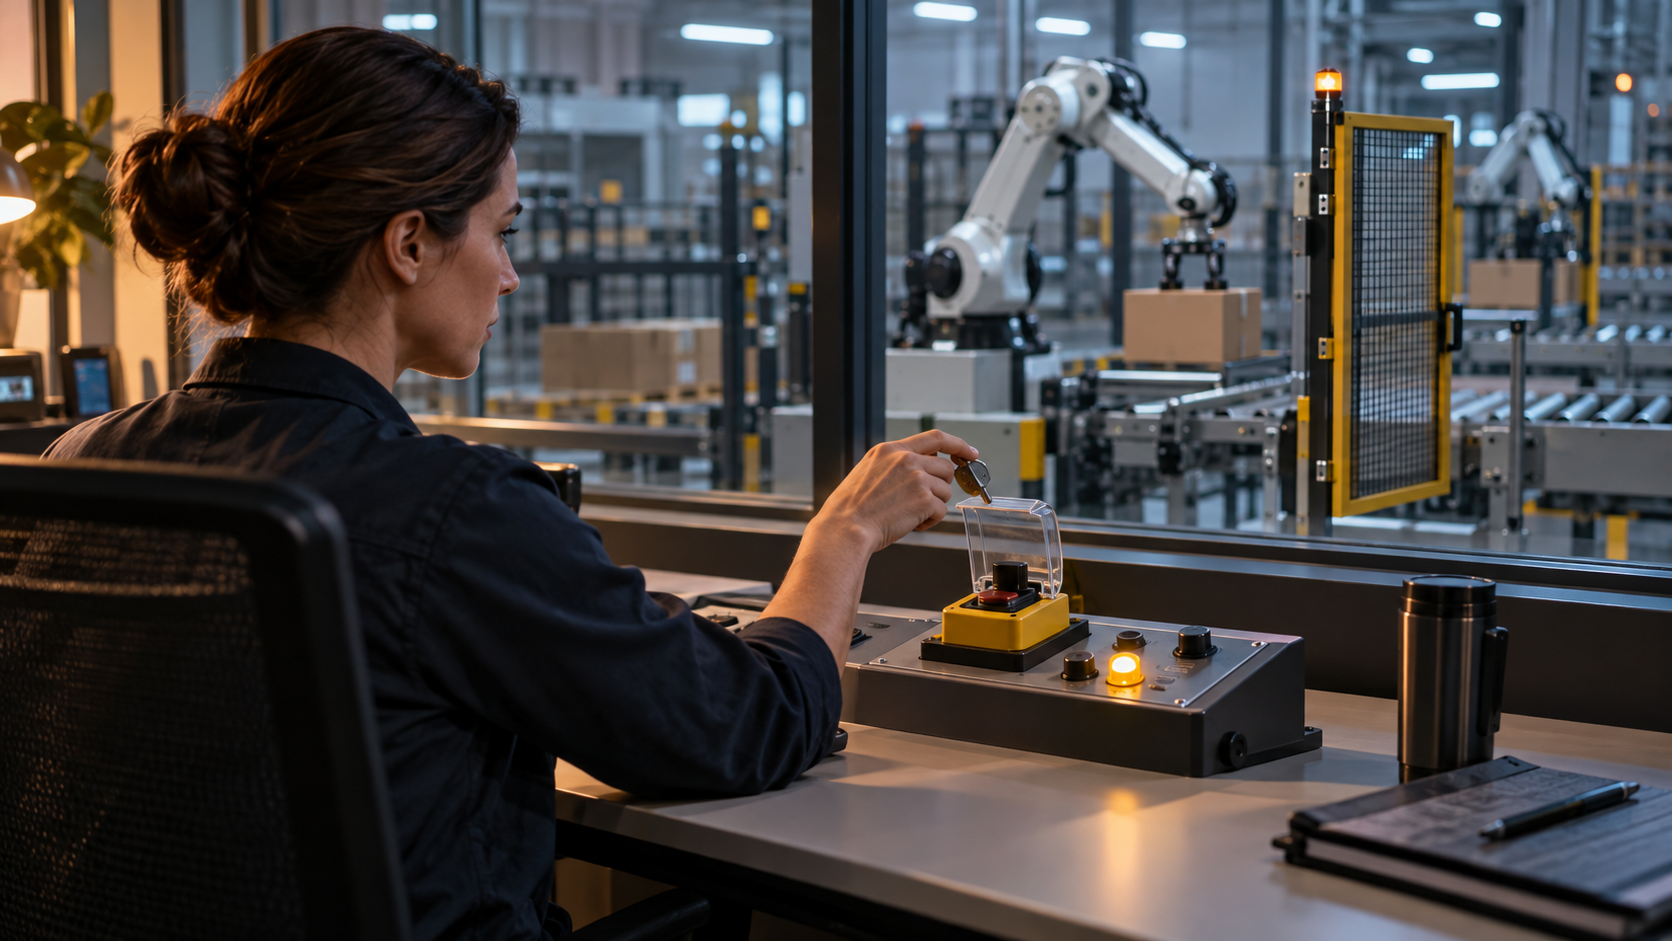
Most software interfaces treat friction as a defect. Fewer clicks, fewer confirmations, fewer interruptions: these are familiar signs of polish. Apply that logic mechanically to AI agents, however, and a smooth experience can become an unsafe one.
An agent does not merely display information. It can search private systems, modify files, contact customers, approve expenses, deploy software, and create obligations. When a product removes every pause between intention and execution, it also removes the moments when a person can detect that the system misunderstood the assignment.
The answer is not a confirmation dialog before every tool call. That produces habituation, and habituation turns “Approve” into a reflex. The answer is to place gates where consequences change category.
Permission should follow impact, not technical capability
Developers often design authorization around tools: this agent can access email, that one can access a database, another can run shell commands. Tools are necessary security boundaries, but they are poor descriptions of human risk. The same email tool can search an inbox, draft a response, or send a contractual promise. Those actions should not share one permission simply because they use the same API.
A better model starts with effects. Is the action reversible? Does it expose data to a new party? Does it spend money? Does it alter a system of record? Does it communicate as the user? Could repetition multiply the impact? The answers define a risk tier, and the risk tier determines whether the agent may proceed silently, must preview its plan, or needs explicit approval.
OpenAI’s paper on governing agentic systems frames safe operation as a lifecycle responsibility rather than a property of the underlying model. That distinction is crucial. Even an unusually capable model cannot infer every organization’s authority structure, contractual limits, or tolerance for irreversible action. The application must encode them.
This leads to a simple product rule: autonomy should expand inside a bounded workspace and contract at its edges. Let an agent inspect, compare, calculate, and draft freely in a sandbox. Stop it when work crosses into publication, payment, deletion, deployment, or disclosure.
A useful gate explains the decision
Many approval screens show a vague message—“The assistant wants to take an action”—followed by technical parameters. That is not informed consent. It transfers interpretation work back to the user at precisely the moment the product should be clearest.
A good gate answers four questions in plain language:
- What will happen?
- Which resources or people will be affected?
- Why does this action advance the user’s request?
- What can be undone afterward?
The preview should emphasize the delta. For a database update, show the records and fields that will change. For a code deployment, show the environment, revision, checks, and rollback route. For an outbound message, show recipients and final content. Approval is meaningful only when the user can see the consequence without reconstructing it from logs.
Anthropic’s guide to building effective agents recommends simple, composable patterns and describes agents as systems that receive environmental feedback in a loop. The interface should make that loop legible. Users need not watch every internal step, but they should be able to inspect the plan, evidence, completed actions, and current boundary.
Do not ask humans to supervise machine-speed noise
Human oversight is often invoked as if adding a person automatically makes automation safe. It does not. A reviewer faced with hundreds of low-context prompts becomes a slow, unreliable rubber stamp. Effective oversight requires scarcity: reserve human attention for decisions where judgment changes the outcome.
That means low-risk actions need policy-based preauthorization. A finance agent might categorize transactions and prepare reconciliation notes autonomously, while any transfer requires approval. A support agent might retrieve policy and draft replies, while refunds above a defined threshold or messages containing unusual commitments are escalated. A coding agent might edit and test within a branch, while production deployment and secret access remain gated.
Escalation rules should also account for uncertainty. When an agent’s plan depends on an ambiguous identity, conflicting instruction, missing evidence, or surprising tool result, it should stop even if the nominal action is usually permitted. Anomaly is itself a risk signal.
After approval, the system needs receipts. An action log should record what was proposed, what the user authorized, what actually occurred, and whether later compensation or rollback changed the state. This is not just compliance infrastructure. It is the foundation for debugging trust: when something goes wrong, teams can distinguish model error, stale context, tool behavior, policy failure, and mistaken human approval.
Trust comes from controlled momentum
The best agent experience does not feel obstructive. It feels like a competent colleague who knows which decisions are theirs to make and which belong to you. It moves quickly through analysis, pauses before commitment, and presents the choice with enough context to act confidently.
This is why blanket autonomy is a weak product goal. Users do not want software that acts without them; they want work to advance without losing control. Those are different ambitions.
At XioX, we view the approval boundary as a first-class interface component, alongside navigation, search, and editing. It deserves user research, instrumentation, and repeated testing. Teams should measure unnecessary interruptions, rejected proposals, approvals later reversed, and incidents that passed through a gate. Those signals reveal whether the boundary is correctly placed.
A capable agent creates momentum. A trustworthy product shapes that momentum with explicit authority, visible consequences, and well-timed restraint. The gate is not where intelligence ends. It is where responsible agency begins.
Advertisement


